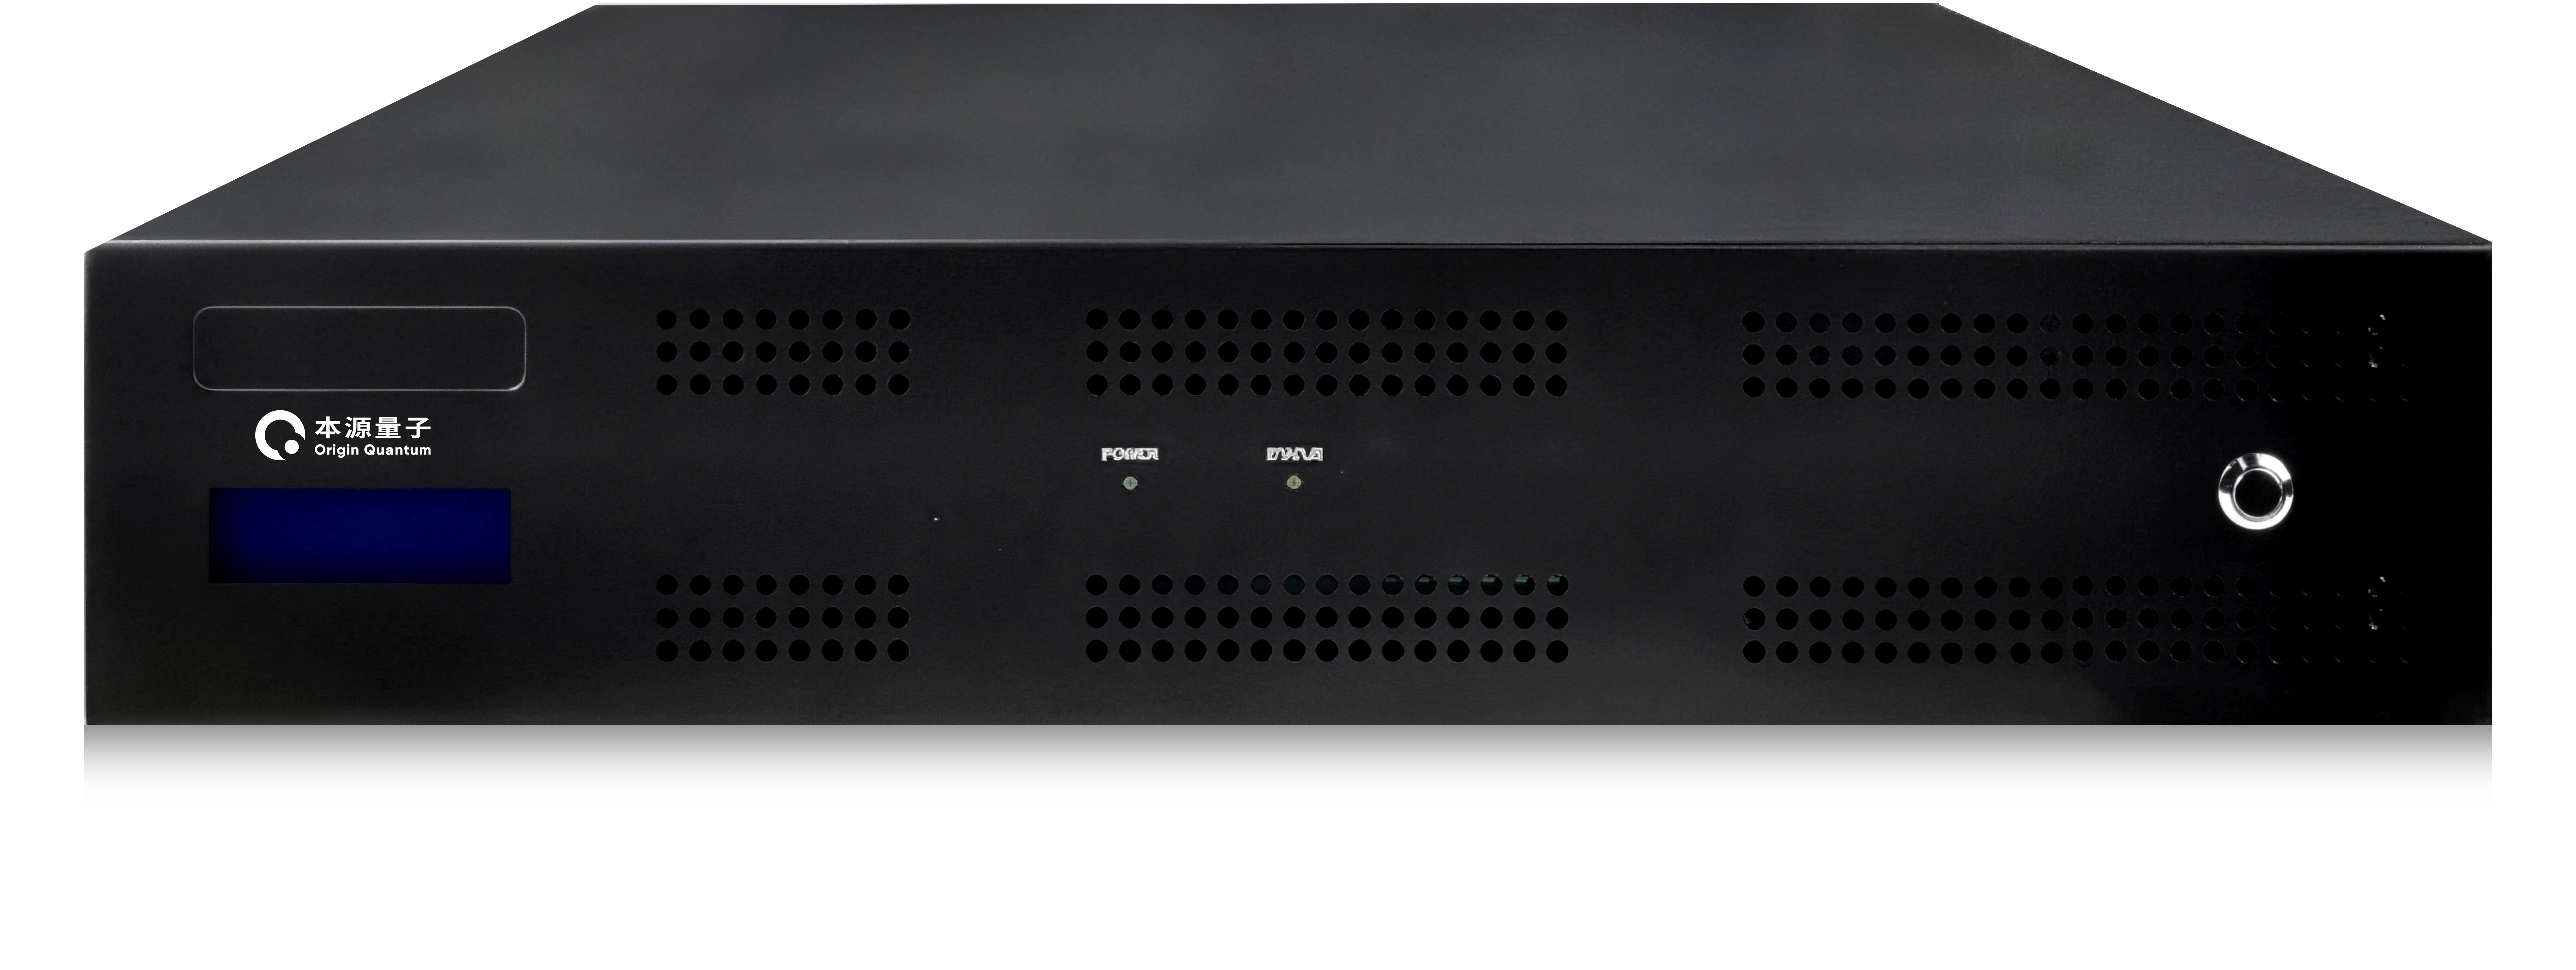
Origin Rock — Post-Quantum Server Cryptographic Machine
Origin Rock — Post-Quantum Server Cryptographic Machine
As a core infrastructure device, the post-quantum server cryptographic machine provides secure computing and key support for scenarios such as government affairs and finance, effectively preventing data leakage, key theft and authority abuse.
Product Description
Product Functions
Comprehensive algorithm support.
- Supports the SM2 national cryptographic standard algorithm.
- Supports national cryptographic standard symmetric algorithms such as SM1 and SM4.
- Supports hash algorithms such as SM3.
- Supports PQC key encapsulation algorithms such as ML-KEM512, ML-KEM768, and ML-KEM1024.
- Supports PQC signature, verification, and identity authentication algorithms such as ML-DSA44, ML-DSA65, and ML-DSA87.
- Supports a quantum random number generator to generate true quantum random numbers.
Three-level key protection + IP whitelist, ensuring full lifecycle security of keys.
Active-standby mode + redundant power supply, ensuring high availability and uninterrupted operation.
High Maintainability
It is equipped with extended functions such as log audit, status monitoring, SNMP standard protocol monitoring, SYSLOG log forwarding, and NTP time synchronization, which further improves the maintainability of the server cryptographic machine.
Application Scenarios
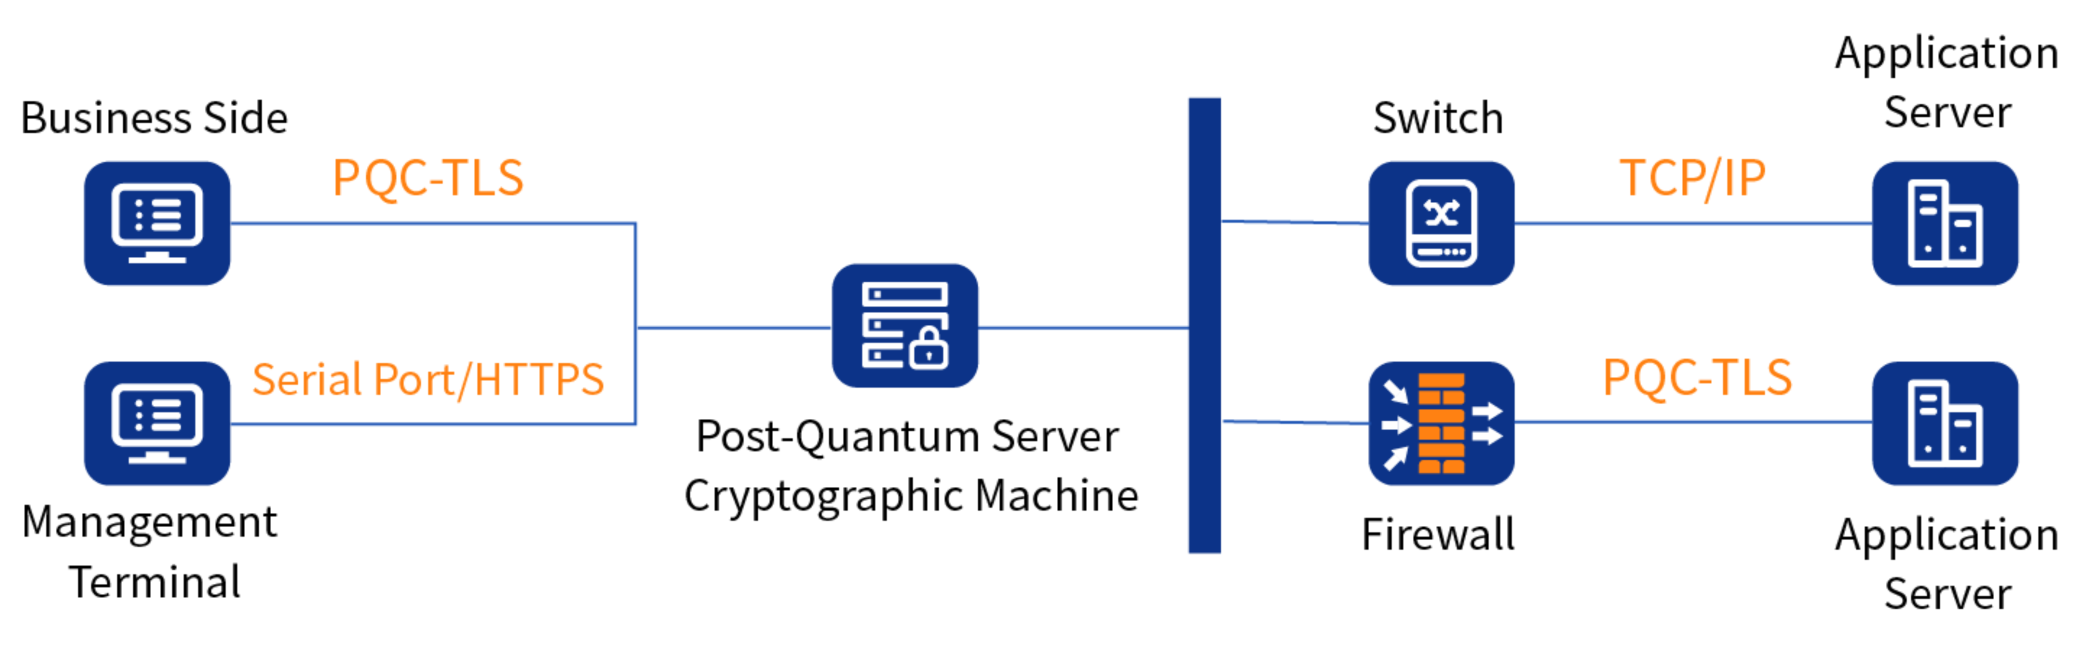
The post-quantum server cryptographic machine is deployed together with management terminals, switches, firewalls, and application servers.
 Management Terminal
Connect to the web management interface of the post-quantum server cryptographic machine via serial port, HTTPS and other protocols for management operations.
 Service End
The service end can connect to the cryptographic machine via TCP/IP and PQC-TLS protocols.
 Application Server and Cryptographic Machine
For deployment in the same network, TCP/IP access is recommended; for open network environments, TLS or PQC-TLS is suggested to ensure secure transmission.
Main Technical Parameters
| SM2 Key Pair Generation | ≥16000Tps |
| SM4 Encryption and Decryption | ≥1700Mbps |
| SM3 Encryption and Decryption | ≥1000Mbps |
| ML-KEM Key Pair Generation | ≥25000Tps |
| ML-DSA | ≥11000Tps |
| Quantum Random Number | 20Mbps |
| Others | 2U standard rack-mounted, equipped with redundant AC power supply, 2 Gigabit electrical ports and 2 10-Gigabit optical ports. |